Field notes from the edge.
What our engineers learned this week. Hands-on technical deep-dives, postmortems, and strategy frameworks.
 AI
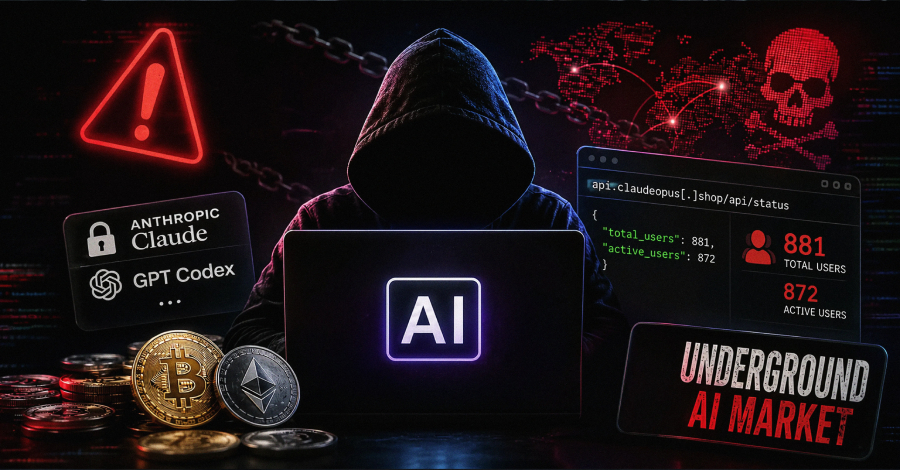
Poison Claude Sells Discounted Claude Access While Its Operator Sees Every Customer Prompt
Cybersecurity researchers have identified multiple illegal services on underground forums selling unauthorized access to AI models, including 'Poison Claude,' which claims to offer discounted access to Anthropic's language models. These services pose significant security risks as operators can intercept and view all customer prompts, creating potential data exposure and intellectual property theft
 AI
AI Harnesses Burst With Potential Exploit Opps
The complex software ecosystem that comprises AI infrastructure introduces significant security vulnerabilities due to trust issues between interconnected components. These trust gaps create potential attack vectors that organizations must address as AI adoption accelerates across enterprise environments.
 AI
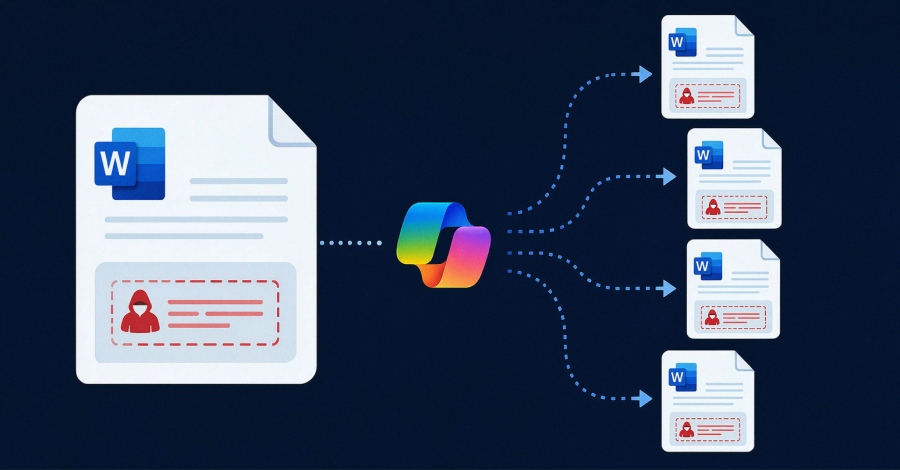
Microsoft Copilot for Word Can Copy Hidden Prompts Into New Documents
A security researcher disclosed a vulnerability in Microsoft 365 Copilot for Word where hidden instructions embedded in documents can manipulate AI-generated content and self-propagate into newly created files. The technique, reported to Microsoft 144 days prior to public disclosure, demonstrates how malicious prompts can persist across multiple document generation sessions, potentially compromisi
 AI
Patch-Resistant 'RufRoot' Flaw Can Unleash Malicious AI Agent Swarms
A critical vulnerability dubbed 'RufRoot' has been discovered in the Ruflo AI hosting platform that allows unauthenticated attackers to gain system control and corrupt memory. The flaw is particularly dangerous because malicious behavior can persist even after security patches are applied, potentially enabling attackers to deploy swarms of compromised AI agents.