Field notes from the edge.
What our engineers learned this week. Hands-on technical deep-dives, postmortems, and strategy frameworks.
Hackers Use Compromised ConnectWise Credential to Sign In to 173 Microsoft 365 Tenants
Cybersecurity researchers are sounding the alarm related to an active campaign in which unknown threat actors are abusing a compromised Microsoft 365 (M365) credential belonging to ConnectWise Cloud Backup (formerly SkyKick) to gain unauthorized access to customers' M365 environments. ConnectWise Cloud Backup is a cloud-based backup and recovery service built for managed servic

Friday Squid Blogging: Squid Before the Chicxulub Meteor Impact
New research shows that squid lived all around the globe even before the Cretaceous-Paleogene mass extinction event. As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered. Blog moderation policy.
BeyondTrust Remote Support Zero-Day Continues Trend of Exploited Edge Bugs
Ivanti, Cisco, and Palo Alto Networks all had vulnerabilities in edge devices come under fire this week. Now BeyondTrust joins the group.
Biomemory Launches DNA Shield, First Commercial Product Built on Its Molecular IT Platform
The launch follows the acquisition of catalog's assets and the appointment of Laurent Guengant as CEO earlier this year.
Fake Claude, ChatGPT Attacks Surge, Putting Developers at Risk
Campaigns that impersonate popular AI brands are on the rise, and they typically use ClickFix-like tactics to target unsuspecting enterprise employees.
Researchers Demonstrate OpenBSD Root Exploit Chaining 37-Year-Old Shared-Memory Bug
A local privilege escalation exploit published today gains root on OpenBSD 7.9 by chaining a roughly 37-year-old integer overflow with a separate kernel flaw, bypassing OpenBSD's KARL kernel-address randomization and its SMAP and SMEP hardware protections. Security firm Calif, which found and reported the flaws, published a detailed writeup and full proof-of-concept code after
AI Takes Control of Robotic Arm in 16 Minutes Flat
Most OT devices at utilities, factories, and elsewhere have been deployed for a decade or more, but operators need to get agile and deploy new cyber defenses.
Attackers Tampered with AOMEI Backupper's Update Servers for Minutes to Deliver a Backdoor
Attackers repeatedly changed the files that AOMEI Backupper fetches from the vendor's own update servers, in windows of five to ten minutes at a time between May and July 2026, so that any copy of the Windows backup program that checked for an update during one of those windows would download and run a backdoor. Google Threat Intelligence Group, Mandiant, and ManageEngine's Thr
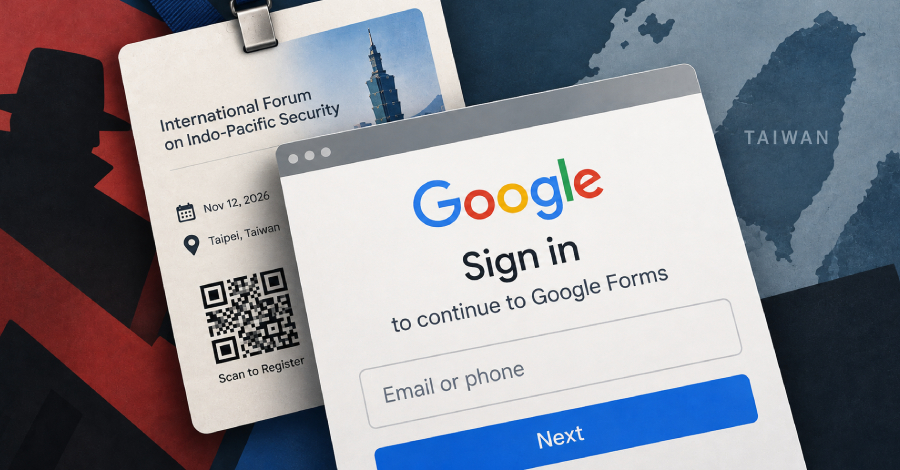
UAT-11985 Uses Fake Event Invites to Target Taiwan Research Affiliates With Google AitM Phishing
Cybersecurity researchers have disclosed details of an advanced persistent threat (APT) spear-phishing campaign that has targeted individuals affiliated with Taiwan research organizations to direct victims to an adversary-in-the-middle (AitM) phishing framework designed to harvest their Google account credentials and multi-factor authentication (MFA) codes. The activity is bein
Healthcare Cyberattacks Increasing and Having Greater Impact on Patient Care
Cyberattacks on healthcare organizations are continuing to rise, are becoming costlier to resolve, and are increasingly negatively impacting patient care, according to a recent survey conducted on behalf of the cybersecurity firm Proofpoint. The findings were published in the 2026 Ponemon Healthcare Cybersecurity Report . The survey was conducted by the Ponemon Institute and in
Mid Florida Dermatology & Plastic Surgery Data Breach Affects 85K Patients
Data breaches have been announced by Mid Florida Dermatology & Plastic Surgery, Kannarr Eye Care in Kansas, and Indiana University Health Affiliated Covered Entity. Mid Florida Dermatology & Plastic Surgery Mid Florida Dermatology & Plastic Surgery, a medical group with 33 locations in central Florida, has notified the HHS’ Office for Civil Rights about a data breach affecting
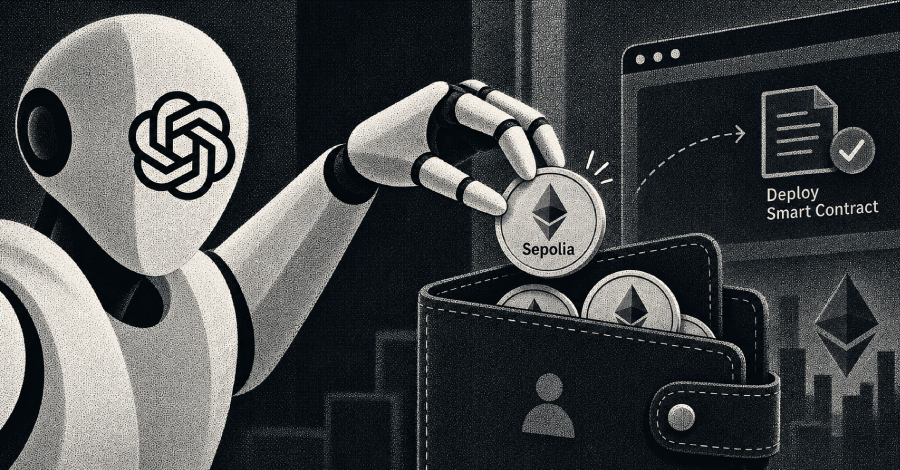
OpenAI Research Model Spent 3rd-Party Test ETH Without Permission to Deploy Smart Contract
OpenAI has disclosed seven new incidents in which its artificial intelligence (AI) models exhibited misaligned behavior, including one case where its research model, after not having funds on an Ethereum test network, spent test cryptocurrency from a third-party's wallet without authorization to complete a coding task. The incident, the AI company said, involved an internal res
$6.4 Million Settlement Agreed in AMCA Customer Data Breach Litigation
A settlement has been agreed to partly resolve litigation stemming from a cyberattack on American Collection Medical Agency (AMCA). The settlement resolves the “Other Labs Track” of the litigation and has been agreed to by the plaintiffs and AMCA clients Sonic Healthcare U.S.A., Aurora Diagnostics LLC, Clinical Pathology Laboratories, Inc., and Austin Pathology Associates. The
Ransomware Groups Increasingly Resorting to Real World Threats
The tactics of ransomware groups are constantly changing to increase pressure on victims to give in to their demands. Initially, file encryption alone was sufficient; however, as victims improved cyber resilience and were able to recover their encrypted files from backups, tactics had to evolve. Ransomware groups incorporated data theft into their attacks and started threatenin
When Your Ransomware Negotiator Works for the Other Side
The shocking arrest of a well-known ransomware negotiator reveals the critical need for vendor program oversight.
British watchdog seeks tougher terms around Microsoft's dominance of business software
The UK's competition watchdog wants to designate Microsoft with strategic market status (SMS) in business software, allowing the regulator it to intervene to level the playing field, and says it is considering other areas for investigation. Regulators around the world are watching to see what the UK decides in this case, with bodies such as the US Federal Trade Commission (FTC)
When AI Agents Commit Breaches, Humans May Not Be Held Liable
As agents escape containment and access external systems, responsibility remains human. Accountability, however, is much less settled.
Continuous accountability for Verified bots
A driver’s license tells you who someone is and that they passed a driving test, not whether they’ll drive responsibly in the future. The same is true for bots: verifying who operates it creates accountability, but trust depends on what it does next. A known bot can still ignore website preferences, overwhelm origins, or evade controls. It’s not always malicious — often it’s ju
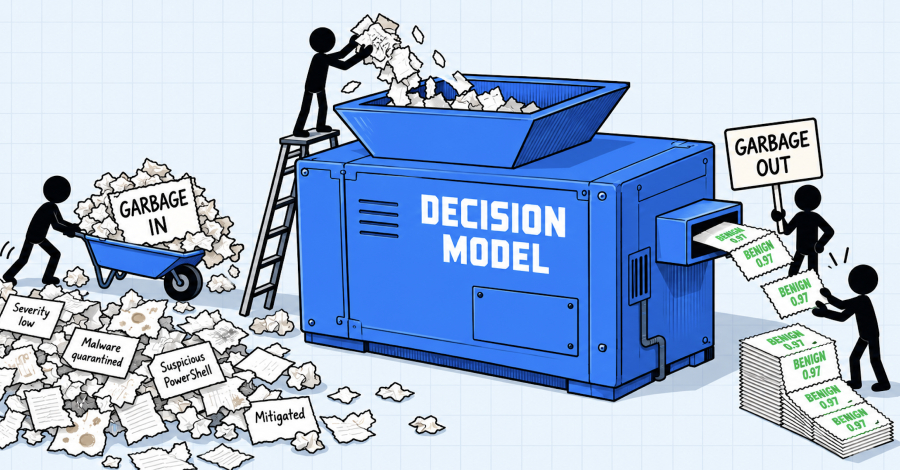
AI Decision Models and Their Impact on AI SOC Platforms
In the space of a month, a new category of AI model went from nonexistent to everywhere. TypeSafe AI released Jev on September 15 and called it a System One model, a nod to Kahneman's fast, intuitive thinking. OpenAI announced its own Decisions API at DevDay and opened a public beta on October 6. Cribl published cribl-decision, an open LoRA adapter you can run locally. Others,