Field notes from the edge.
What our engineers learned this week. Hands-on technical deep-dives, postmortems, and strategy frameworks.
Texas Hospice Management Company Data Breach Affects 35,000 Texas Residents
AngMar Management Services, a Mansfield, Texas-based home health and hospice management company, has identified unauthorized access to its information technology systems. The incident was identified on July 20, 2026, and the forensic investigation determined that an unauthorized individual potentially accessed and/or acquired files containing patient information on or around Ju
OCR Clarifies When SUD Records Can be Used to Verify Medicaid Community Engagement Exclusions
The U.S. Department of Health and Human Services (HHS) Office for Civil Rights (OCR) has issued guidance for state Medicaid Agencies clarifying when the Part 2 regulations permit Medicaid applicants’ or beneficiaries’ SUD records to be used to verify an exclusion from the community engagement requirement for Medicaid eligibility. The Confidentiality of Substance Use Disorder (S
Data Breaches Announced by Saber Healthcare & Buchalter
Data breaches have been announced by Saber Healthcare in Ohio and Buchalter, a California-headquartered law firm that provides services to Arrowhead Regional Medical Center. Bright Smile Dental Care in Indiana has fallen victim to a ransomware attack, although unauthorized access to patient data is considered unlikely. Saber Healthcare Saber Healthcare, a Beachwood, Ohio-based
CPAP Medical Supplies and Services Agrees to Pay Up to $500K to Resolve Data Breach Lawsuit
CPAP Medical Supplies and Services, a Jacksonville, Florida-based provider of durable medical equipment for treating sleep apnea, has agreed to pay up to $500,000 in benefits to individuals affected by a December 2024 cyberattack and data breach. The cybersecurity incident was identified in late December 2024, and the forensic investigation determined that an unauthorized third
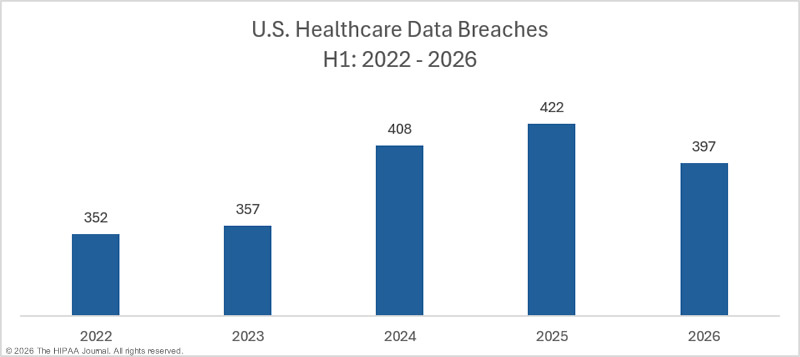
H1 2026 Healthcare Data Breach Report
There has been a 5.9% decline in healthcare breaches compared to H1 2025. Between January 1 and June 30, 2026, 397 data breaches affecting 500 or more individuals were reported to the U.S. Department of Health and Human Services (HHS) Office for Civil Rights – the lowest H1 total since 2023. While the year-over-year reduction in healthcare data breaches is a step in the right d
DC Medicaid Agency Notifies 400,000 Beneficiaries About Data Exposure
Almost 400,000 Medicaid beneficiaries in the District of Columbia have had personal and protected health information exposed online, according to a recent disclosure by DC’s Medicaid agency. On July 21, 2026, the District of Columbia Department of Health Care Finance (DHCF) said it discovered two reports had been published on its website that exposed sensitive data to unauthori
The Mental Health Association Data Breach Settlement Agreed
The Mental Health Association, a Chicopee, Massachusetts-based human services agency that provides substance use recovery and support services for developmental disabilities, has agreed to a settlement to resolve class action litigation over a November 2024 cyberattack and data breach that affected 12,633 individuals. Cybercriminal actors breached its network in November 2024 a
Citrix Patches Actively Exploited NetScaler ADC & NetScaler Gateway Vulnerabilities
Two critical zero-day vulnerabilities in Citrix NetScaler ADC (formerly Citrix ADC) and Citrix NetScaler Gateway (formerly Citrix Gateway) are under active exploitation and require immediate patching. The vulnerabilities are part of a batch of eight flaws detailed in a Citrix security bulletin issued on September 27, 2026. Six of the vulnerabilities are rated high severity, wit
WPM Pathology Laboratory; Salina Regional Health Center Settle Class Action Litigation
A settlement has been agreed to resolve class action litigation over a November 2024 targeted cyberattack on the information systems of WPM Pathology Laboratory. The cyberattack occurred on or around November 4, 2024, and resulted in unauthorized access to sensitive personally identifiable information (PII) and protected health information (PHI). Data compromised in the inciden
OpenAI Agent Hacks Australian Medicare Portal
An artificial intelligence (AI) agent developed by OpenAI gained unauthorized access to an Australian Medicare statistics reporting service portal and obtained non-public data. The same AI agent also accessed three other government systems as part of its autonomous research activities: the web portals of the Australian Institute of Health and Welfare, the Victorian Department o
California Critical Access Hospital Announces Cybersecurity Incident
Data breaches have been announced by Modoc Medical Center and Vista Del Mar Child and Family Services in California, Park Place Behavioral Healthcare in Florida, and Millstone Medical Outsourcing in Massachusetts. Modoc Medical Center Modoc Medical Center, a 12-bed critical access hospital and rural healthcare system based in Alturas, California, has identified unauthorized acc
LabCorp Settles Multistate Data Breach Investigation for $2.3 Million
A coalition of 44 state attorneys general has agreed to settle a multistate investigation of Laboratory Corporation of America (LabCorp) regarding a 2019 data breach at its debt collection company, American Medical Collection Agency (AMCA). LabCorp has agreed to pay $2,287,455, which will be divided among the 44 states participating in the action. AMCA is a subsidiary of the de
Wayne Memorial Hospital; Regional Urology Settle Data Breach Lawsuits
Settlements have been agreed to resolve class action complaints against Wayne Memorial Hospital in Georgia and Regional Urology in Louisiana stemming from breaches of patients’ personal and protected health information. Wayne Memorial Hospital Data Breach Settlement Wayne Memorial Hospital Auxiliary, Inc. d/b/a Wayne Memorial Hospital, a Georgia healthcare provider, has agreed
Data Breaches Announced by MedImpact Healthcare Systems; Rosch Visionary Systems
Notification letters are being mailed to individuals affected by data breaches at the pharmacy benefit management service provider MedImpact Healthcare Systems and the healthcare software company Rosch Visionary Systems. MedImpact Healthcare Systems MedImpact Healthcare Systems, a provider of pharmacy benefit management services to health plans, government entities, and self-in
CVS Health; Criteo Agree to Pay $20.5 Million to Resolve Website Tracking Litigation
Settlements have been agreed to resolve class action litigation against CVS Health & Criteo and American Wellness Corp. The lawsuits stem from their use of tracking technologies on their websites and mobile apps. CVS Health & Criteo Corp. Pixel Settlement A $20.5 million settlement has been agreed to resolve class action litigation against the U.S. healthcare company CVS Health
Data Breaches Announced by Gastroenterology Practice and Hospice Companies
Data breaches have been announced by Gastroenterology & Hepatology of Central New York, Three Oaks Hospice, and Doctor’s Choice Home Care. Gastroenterology & Hepatology of Central New York Gastroenterology & Hepatology of Central New York, a medical practice specializing in digestive disorders and liver disease with locations in Liverpool and Syracuse, has started notifying pat
Oculus Pathology Notifies 20,000 Patients About April 2026 Security Incident
Texas-based Oculus Pathology has disclosed a data breach affecting more than 20,000 patients. Data breaches have also been announced by Paradigm Healthcare Services in California and LeMaitre Vascular in Massachusetts. Oculus Pathology, Texas Oculus Pathology, an Austin, Texas-based anatomic and clinical pathology laboratory that provides services to hospitals, ambulatory surge
California Seeks to Implement AI Guardrails for Mental Health Treatment
A bill has been unanimously passed by the California Senate that seeks to establish common-sense guardrails for artificial intelligence (AI) use in mental health treatment. The bill, SB-903 Mental health professionals: artificial intelligence , was authored by Senator Steve Padilla and seeks to protect individuals seeking therapy or psychotherapy services in the state of Califo
77% of Ransomware Groups Are Targeting the Healthcare Sector
A new analysis of ransomware activity reveals broad, consistent targeting pressure across the United States. Ransomware activity is not limited to any specific industry, with all sectors attacked to varying degrees. The analysis was conducted by the AI-driven cybersecurity and threat intelligence platform provider Anomali, with the findings published in its US Ransomware Indust