Field notes from the edge.
What our engineers learned this week. Hands-on technical deep-dives, postmortems, and strategy frameworks.
 AI
New Interrupt Injection Attack Can Bypass Spectre v2 Defenses on Intel and AMD CPUs
MIT CSAIL researchers have discovered a new attack called INTERRUPT INJECTION that can bypass Spectre v2 defenses on Intel and AMD CPUs. The attack exploits a timing vulnerability where an unprivileged Linux program can inject a hardware interrupt between the processor sanitizing its branch predictor and the kernel using it, effectively re-poisoning the predictor after security measures have been
 AI
New OVSwrap Linux Kernel Flaw Lets Local Users Gain Root via Open vSwitch
A critical memory corruption vulnerability (CVE-2026-64531, dubbed 'OVSwrap') in the Linux kernel's Open vSwitch datapath allows local users to escalate privileges to root access. The flaw affects numerous default-configured Linux distributions, with a public exploit already available covering approximately 800 kernel builds, posing significant risk to enterprise environments running Open vSwitch.
 AI
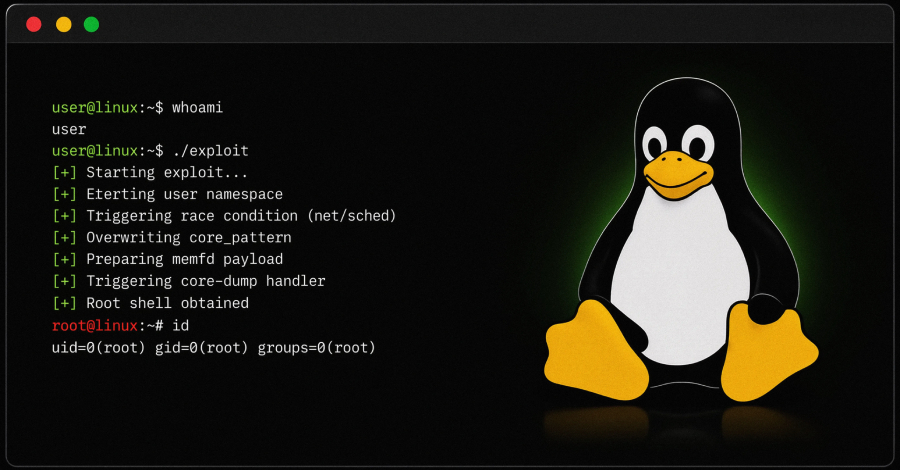
Researcher Says AI Helped Develop Linux Traffic-Control Race Into Root Exploit
STAR Labs disclosed CVE-2026-53264, a high-severity Linux kernel vulnerability in the network traffic-control subsystem that allows local privilege escalation to root on CentOS Stream 9. The researcher utilized AI to accelerate both vulnerability discovery and exploit development, demonstrating AI's growing role in security research.
 AI
Over 400 Arch Linux AUR Packages Hijacked to Deploy Infostealer and eBPF Rootkit
Over 400 packages in Arch Linux's Arch User Repository (AUR) were compromised this week through hijacked build scripts that deployed credential-stealing malware. The Rust-based infostealer targets developer secrets and can deploy an eBPF rootkit when executed with root privileges to evade detection.
 AI
400+ Arch Linux AUR Packages Hijacked to Install Rust Credential Stealer
Over 400 packages in Arch Linux's Arch User Repository (AUR) were compromised this week when attackers hijacked them and modified build scripts to deploy credential-stealing malware. The malicious payload is a Rust-based binary designed to harvest developer credentials and secrets, with the capability to deploy an eBPF rootkit when executed with root privileges to evade detection.
 AI
VerdantBamboo Deploys BSD Variant of BRICKSTORM on Linux Appliances
China-linked cyber espionage group VerdantBamboo has been observed deploying a BSD variant of the BRICKSTORM backdoor along with PLENET (GRIMBOLT) and AGENTPSD malware to target Linux systems. Volexity attributes this activity to VerdantBamboo, which overlaps with Microsoft's Clay Typhoon threat group. This represents an expansion of the threat actor's capabilities to target BSD and Linux-based ap