Field notes from the edge.
What our engineers learned this week. Hands-on technical deep-dives, postmortems, and strategy frameworks.
 AI
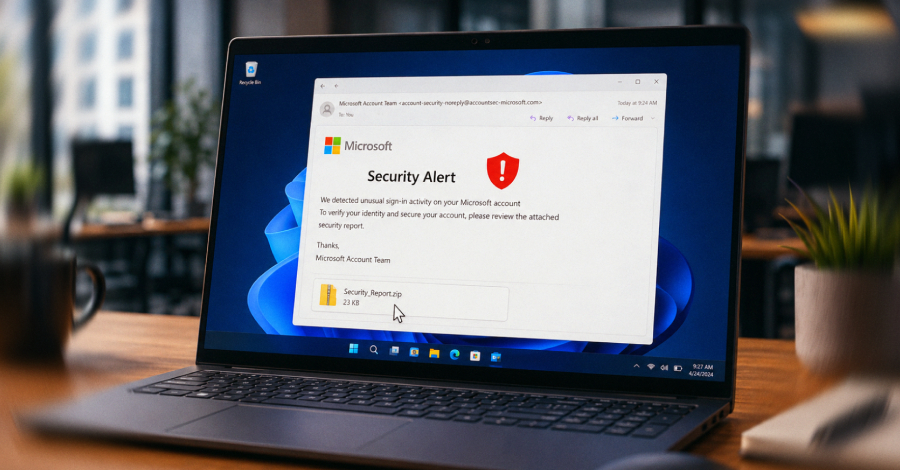
Fake Microsoft Alerts Used to Deploy North Korean NarwhalRAT Malware
North Korean state-sponsored threat actor ScarCruft (APT37) is conducting spear-phishing campaigns that impersonate Microsoft Account security alerts to distribute NarwhalRAT malware. The social engineering tactic leverages fake security notifications to create urgency and trick recipients into executing malicious payloads. This campaign demonstrates continued evolution in APT37's tactics targetin
 AI
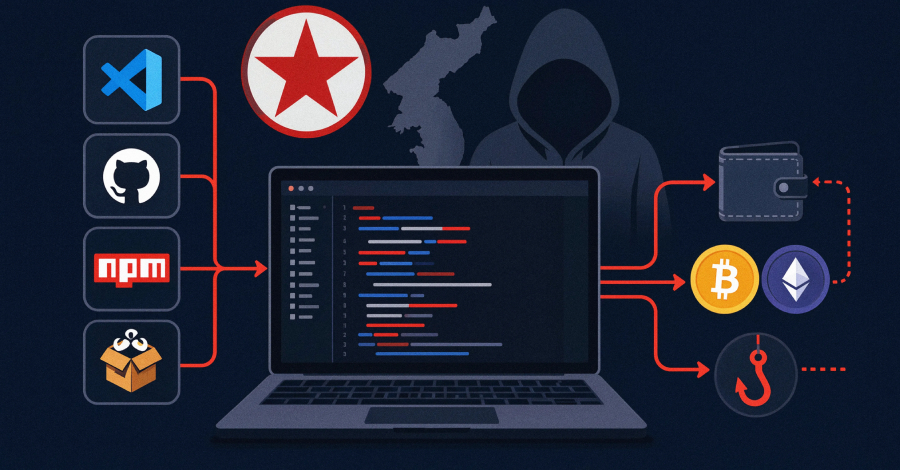
North Korean Hackers Are Turning Developer Tools Into Malware Delivery Channels
Cybersecurity researchers at Proofpoint have identified two malicious campaigns linked to the North Korean threat group Contagious Interview, which is targeting developers through fake recruitment and code review schemes. The threat actor is weaponizing developer tools and processes to deliver malware via sophisticated phishing operations. This represents an evolution in North Korean cyber tactics