Field notes from the edge.
What our engineers learned this week. Hands-on technical deep-dives, postmortems, and strategy frameworks.
ShinyHunters Extorted Boeing Spin-off Prior to Arrests
A teenager from Amman, Jordan suspected of leading the prolific data theft and extortion group ShinyHunters has been detained and is reportedly cooperating with the FBI to identify other members of the hacking gang. KrebsOnSecurity has learned that the suspect, who uses the hacker handle “ Rey ,” was detained as ShinyHunters was in the process of extorting a business unit recen
Dutch Police Arrest ‘Reformed’ Hacker in Shiny Hunters Investigation
Authorities in the Netherlands have arrested a 23-year-old convicted cybercriminal on suspicion of aiding in data thefts and extortions by the prolific hacker group ShinyHunters . In the days immediately following the suspect’s arrest, remaining ShinyHunters members dramatically escalated their attacks, stealing highly sensitive data from the FBI and extorting the Russian ranso
U.S. Soldier Gets 70 Months in Prison for AT&T, Verizon Extortions
A U.S. Army soldier who pleaded guilty to hacking into multiple telecommunications companies and stealing mobile call and text metadata for more than 100 million AT&T customers in 2024 was sentenced to 70 months in federal prison today and ordered to pay nearly $300,000 in restitution to victims. One of several selfies from the Facebook page of Cameron Wagenius. Cameron John Wa
Data Broker Radaris Loses Domains in Privacy Fight
The consumer data broker Radaris.com has long had a reputation for ignoring requests to remove personal information from its vast empire of people-search services online. That reputation caught up with the company recently in a lawsuit alleging Radaris violated a New Jersey privacy law that provides for hefty fines against data brokers that publish personal information on state
Microsoft Plugs Nearly 1,000 Security Holes
Microsoft Corp. today issued updates to plug at least 974 security holes in its Windows operating systems and other software, by far its biggest single patch batch ever. Microsoft says artificial intelligence is helping to speed the discovery of vulnerabilities, but security experts warn that many organizations already are struggling to prioritize the more human-intensive endea
FBI Probes Service Selling 153M+ Drivers Licenses
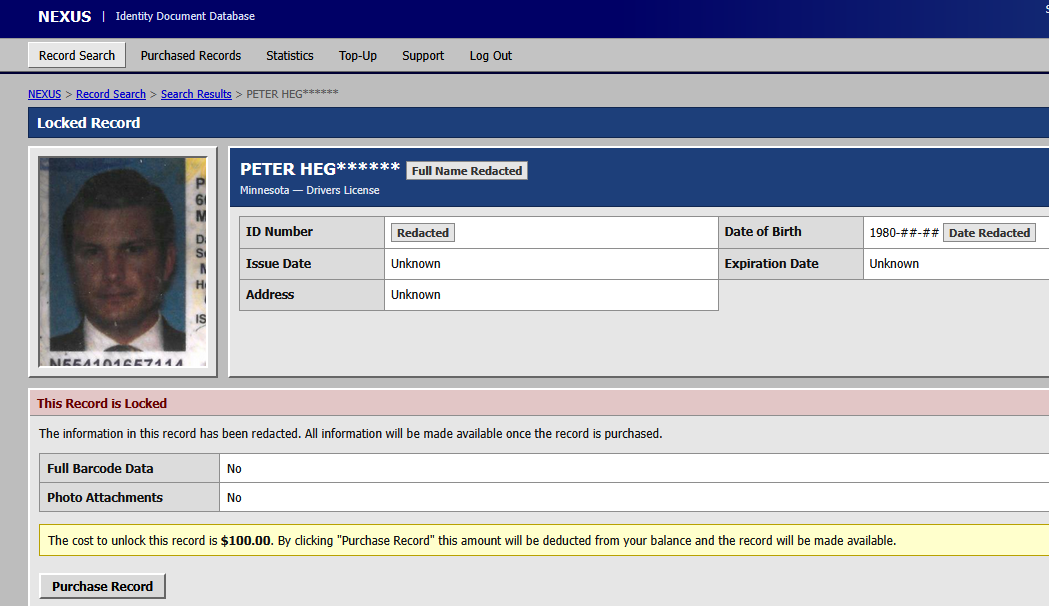
A new identity theft service launched on the dark web this week is selling digital scans of more than 153 million drivers licenses from people in the United States and Canada. Based on interviews with individuals whose licenses are available for purchase on this service, it appears to be siphoning images collected by a widely-used identity verification company based in Louisian
Two Alleged ‘TeamPCP’ Hackers Arrested in Australia
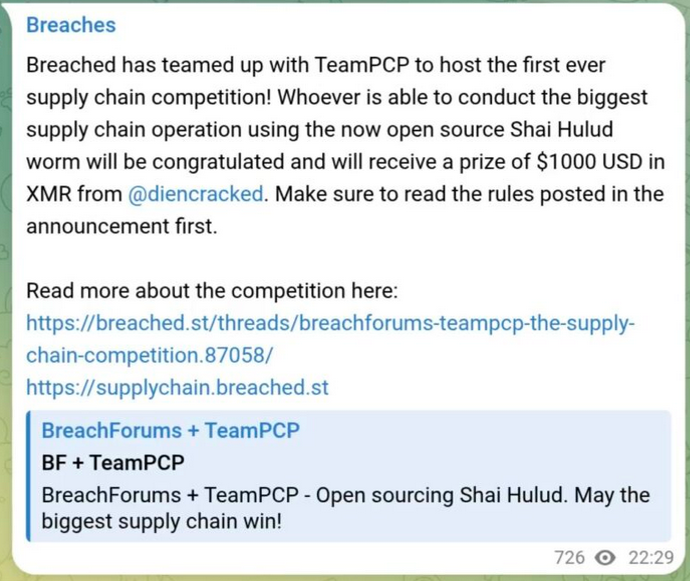
Authorities in Australia have arrested two men believed to be members of TeamPCP , a prolific cybercrime and data extortion group blamed for perpetrating the longest running spree of software supply chain attacks ever. In a statement released today, the Australian Federal Police (AFP) said two unnamed suspects from Western Australia, aged 21 and 23, were arrested in connection
 AI
Who’s Tracking You? Use This New Service to Find Out
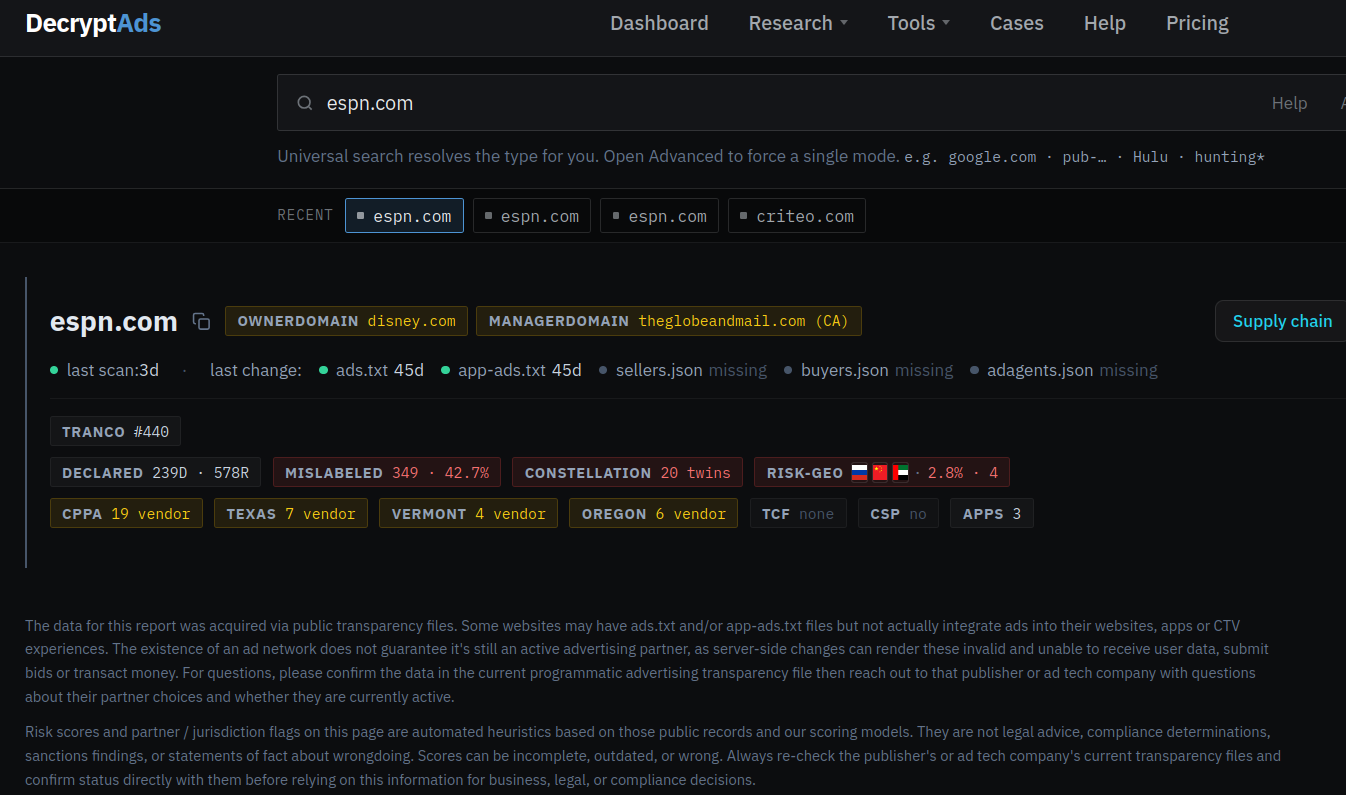
DecryptAds is a new free service that aggregates and correlates publicly available adtech data from ads.txt, app-ads.txt, and related files to reveal which companies are tracking users and serving ads across websites and mobile apps. The platform enables security researchers and privacy advocates to identify malicious ad networks, detect adversarial nation-state tracking, and uncover complex suppl
 AI
Microsoft Plugs Nearly 400 Security Holes
Microsoft released patches for 398 security vulnerabilities in August 2024, including one actively exploited zero-day flaw and two publicly disclosed vulnerabilities. The patch volume surge is attributed to AI-assisted vulnerability discovery, though research shows AI-generated patches fail to properly fix flaws more than half the time. Security experts recommend organizations maintain measured pa
 AI
Canadian Man Pleads Guilty in Snowflake Extortions
Connor Riley Moucka, a 26-year-old Canadian cybercriminal, has pleaded guilty to orchestrating a massive data breach campaign targeting over 165 Snowflake cloud storage customers, including AT&T, TicketMaster, and other major enterprises. The attacks exploited accounts lacking multi-factor authentication, resulting in the theft of billions of sensitive customer records and over $2.5 million in ran
 AI
Read This Before You Buy That TV Streaming Stick
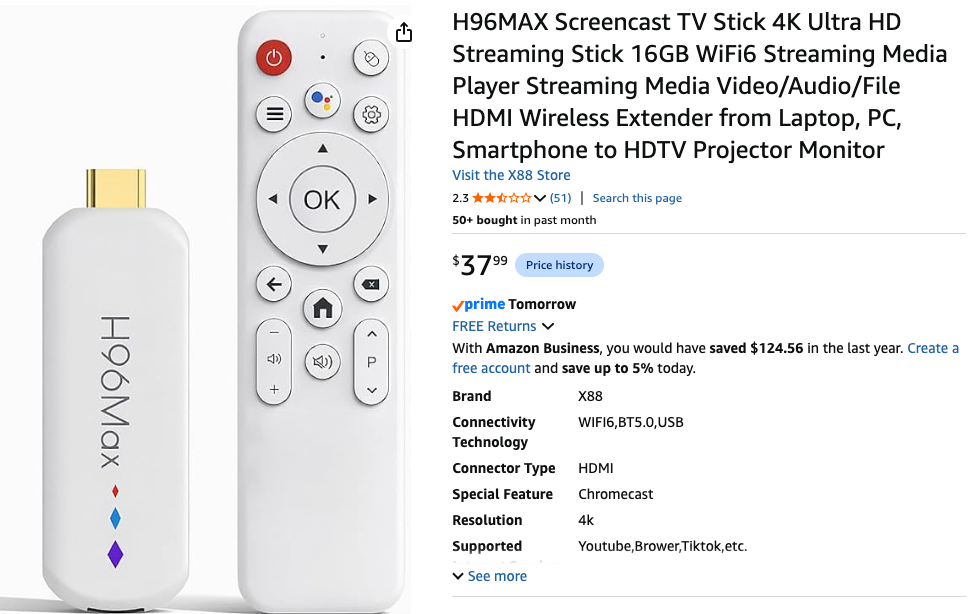
Security researchers at Bitsight have uncovered a sophisticated ad fraud operation embedded in popular H96 TV streaming devices that spoofs mobile phones to click ads on AI-generated websites while simultaneously renting out users' internet connections as residential proxies. The operation, traced to mainland China-based Zhejiang Fengwo IoT Technology Ltd, uses Google's Blockly visual programming
LG to Ban Residential Proxies from Smart TV Apps
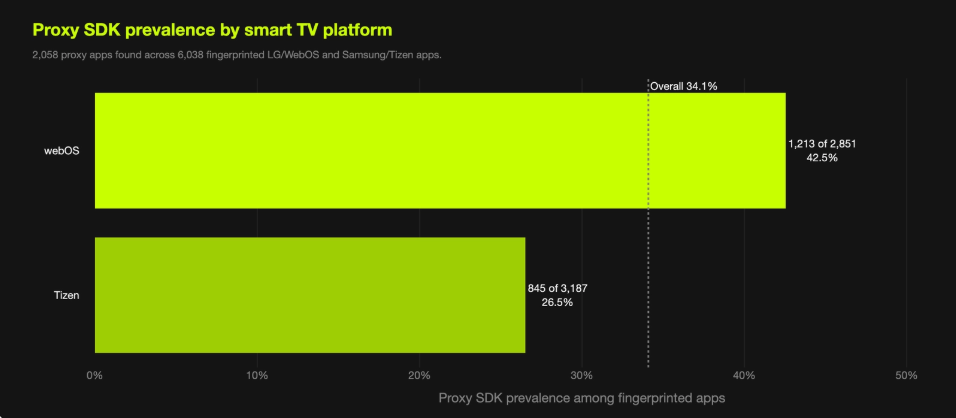
The home appliance giant LG Electronics USA said this week it plans to suspend any apps built for its smart TVs that turn one’s television into an always-on residential proxy node. The move comes less than a month after researchers found that more than 42 percent of games and other apps available for download on LG’s webOS store allow unknown third-parties to route their Intern
Microsoft Patches a Record 570 Security Flaws
Microsoft Corp. today released software updates to plug at least 570 security holes in its Windows operating systems and other software, almost triple the number of vulnerabilities the software giant fixed in its record-smashing Patch Tuesday release last month. Microsoft attributed the burgeoning patch counts to vulnerability discoveries aided by artificial intelligence. Nearl
Lessons Learned from CISA’s Recent GitHub Leak
The Cybersecurity and Infrastructure Security Agency (CISA) has issued a postmortem on a recent data leak in which a contractor published dozens of internal CISA credentials — including AWS Govcloud keys — in a public GitHub repository for almost six months before being notified by KrebsOnSecurity. Experts say the gaps identified in the agency’s initial response provide importa
Felons, Fraudsters Flog Offensive Cybersecurity Startup
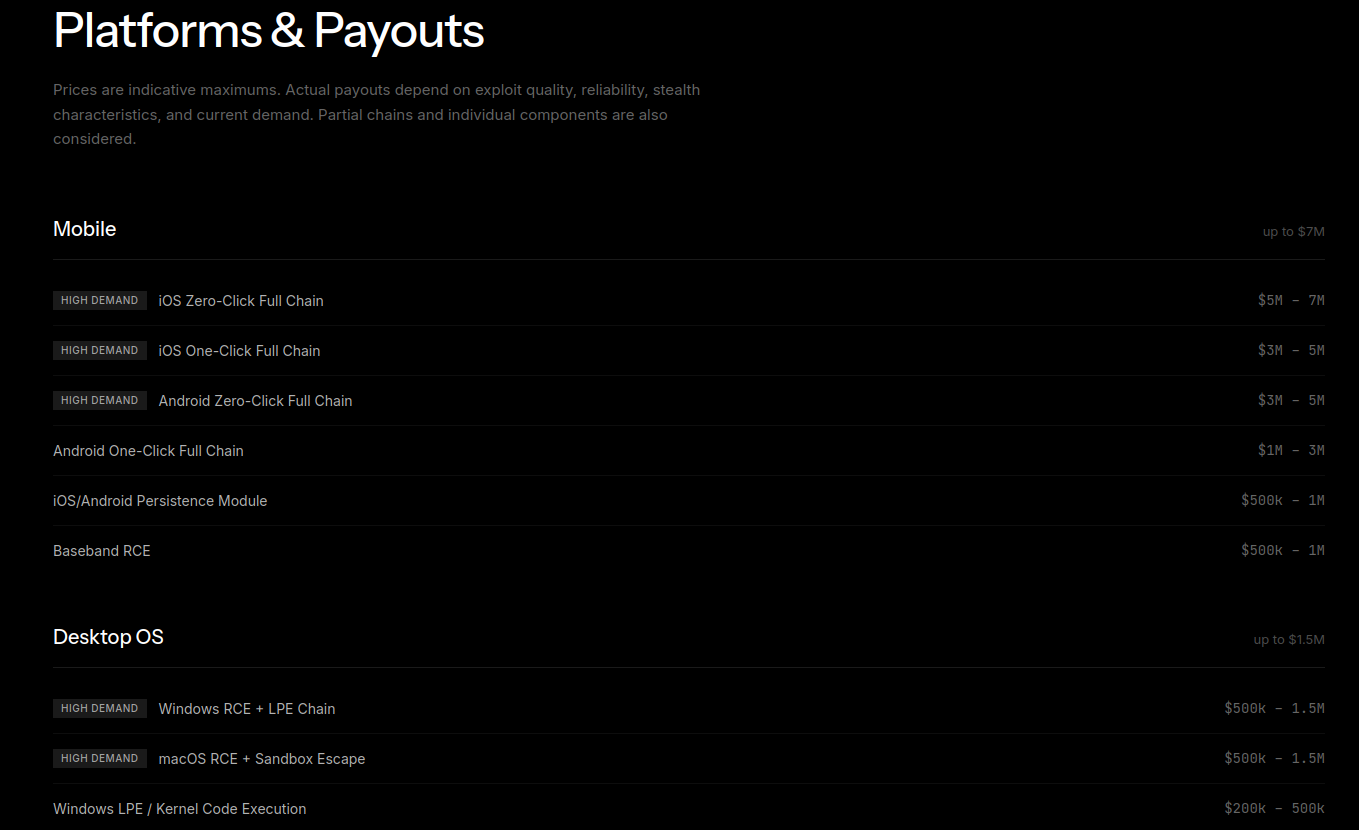
A cybersecurity startup dangling millions of dollars to acquire zero-day security vulnerabilities in popular software is run by a pair of far-right conspiracy theorists and convicted felons whose most recent ventures included fake intelligence companies and a now-defunct AI-based lobbying platform they operated under assumed names. The X/Twitter account IRIS C2 (@C2IRIS) has ga
FBI Seizes NetNut Proxy Platform, Popa Botnet
The Federal Bureau of Investigation (FBI) said today it worked with industry partners to seize hundreds of domains associated with NetNut , a sprawling residential proxy service operated by the publicly-traded Israeli company Alarum Technologies [NASDAQ: ALAR]. The action comes roughly two weeks after KrebsOnSecurity published findings from multiple security firms connecting Ne
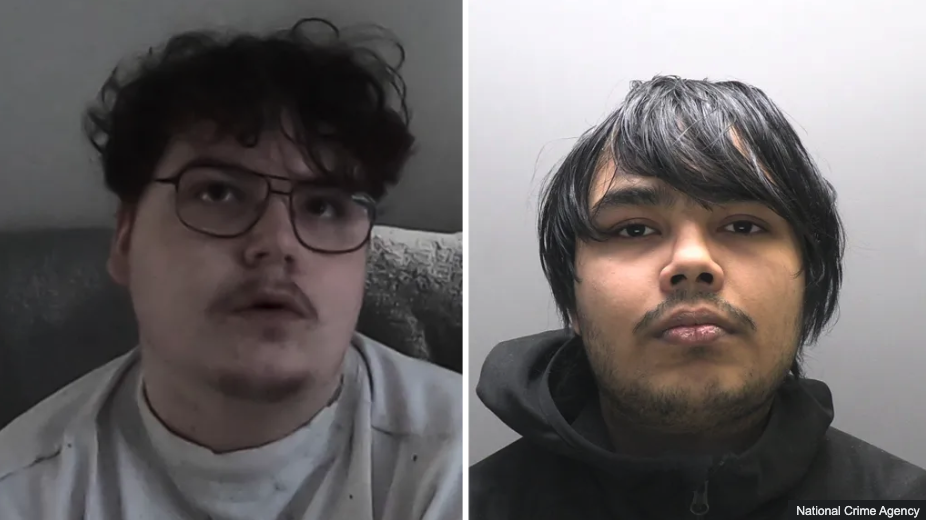
Scattered Spider Hackers Plead Guilty on Day 1 of Trial
Two men pleaded guilty in the United Kingdom this week to criminal charges stemming from an August 2024 cyberattack that crippled Transport for London , the entity responsible for the public transport network in the Greater London area. The duo were key members of a prolific cybercrime group known as Scattered Spider , and their guilty pleas came on the first day of what was ex
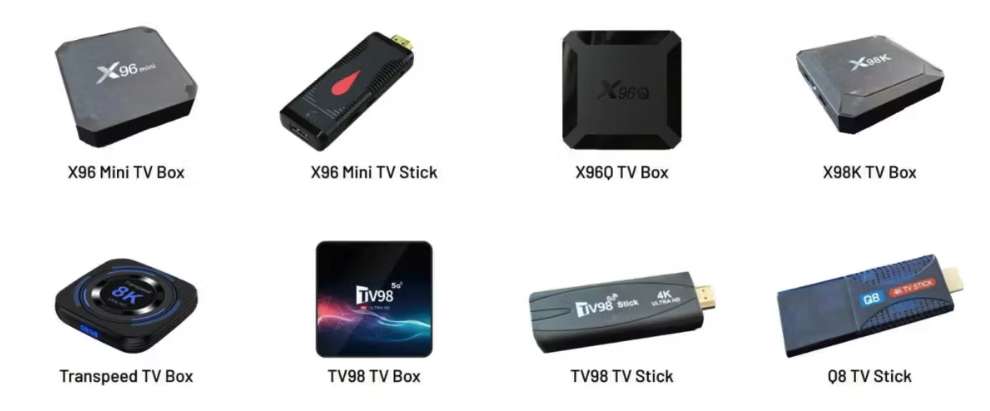
‘Popa’ Botnet Linked to Publicly-Traded Israeli Firm
For the past four years, a sprawling Android-based botnet called Popa has forced millions of consumer TV boxes to relay Internet traffic linked to advertising fraud, account takeovers, and mass data-scraping efforts. This week, researchers from multiple security firms concluded that the Popa botnet is linked to NetNut , a “residential proxy” provider operated by the publicly-tr
 AI
Who Runs the Ransomware Group ‘The Gentlemen?’
The Gentlemen ransomware group has become the second most active ransomware operation by victim count, attracting affiliates with an unprecedented 90/10 revenue split. Security researchers have traced the group's administrator, known as Hastalamuerte/Zeta88, to Alexander Andreevich Yapaev, a 36-year-old from Izhevsk, Russia, who also works in B2B marketing for an electrical products company. The i