Amazon CloudWatch now offers CloudWatch Omni, an AI-powered observability experience for the applications and AI agents you run together. You reach Omni through a dedicated URL for your organization and sign in with the identities you already manage, so working in Omni does not require access to the AWS Management Console. Omni is built on OpenTelemetry: the telemetry you already send to CloudWatch appears in Omni with nothing to reconfigure, and any other workload you instrument with OpenTelemetry sends its telemetry to an OpenTelemetry Protocol (OTLP) endpoint.
CloudWatch Omni offers both agent observability and application observability in a single experience. In our companion post , we introduced the agent observability capabilities of Omni for generative AI and agentic workloads. In this post, we present the application observability experience.
Engineering teams spend a significant portion of their observability time maintaining dashboards, tuning thresholds, and switching between tools to piece together what happened during an incident. When an issue crosses team boundaries, context gets lost in Slack threads and screenshots rather than flowing naturally to the next engineer. CloudWatch Omni changes this by organizing observability around your applications rather than individual signals, and bringing your whole team into the same workspace.
What CloudWatch Omni brings CloudWatch Omni addresses three problems that engineering teams told us they face today. One collaborative experience for your whole team. Every engineer accesses CloudWatch Omni through a single URL with enterprise SSO (via IAM Identity Center , supporting Okta, Azure AD, and other providers).
No AWS Console access is required. SREs, developers, database engineers, and managers share the same data and investigation context. When an investigation escalates, the next person joins the same session with full context already in front of them.
The system adapts as your applications evolve. CloudWatch Omni discovers your services, maps dependencies, and adjusts alarms automatically. Instead of manually curating dashboards and tuning thresholds, you declare what matters (availability targets, latency budgets, error rate thresholds) and Omni adapts as your system changes.
When you deploy new services, Omni updates the application topology automatically. AI-powered investigation with Amazon DevOps Agent. Amazon DevOps Agent participates alongside your team in investigation sessions, correlating signals and suggesting next steps.
The agent works from the same telemetry your engineers see, so its suggestions are grounded in the actual state of your application. It identifies correlated events across services, traces root cause paths through your dependency graph, and maintains investigation history for post-incident review. How an investigation works When something breaks, CloudWatch Omni opens an investigation session pre-loaded with context.
Here is a typical incident workflow: An alarm fires on elevated error rates in your checkout service. Omni opens a session showing the service topology, correlated signals (a deployment 10 minutes earlier, increased latency from a downstream payment API), and DevOps Agent’s initial analysis. Your on-call SRE confirms the deployment correlation, pulls in the trace view to identify failing endpoints, and checks if the payment API latency correlates with a capacity limit.
The SRE escalates to the payments team. The payments engineer joins the same session and sees everything found so far, plus DevOps Agent’s correlation with a configuration change in the payment provider’s API gateway. They identify the root cause and roll back.
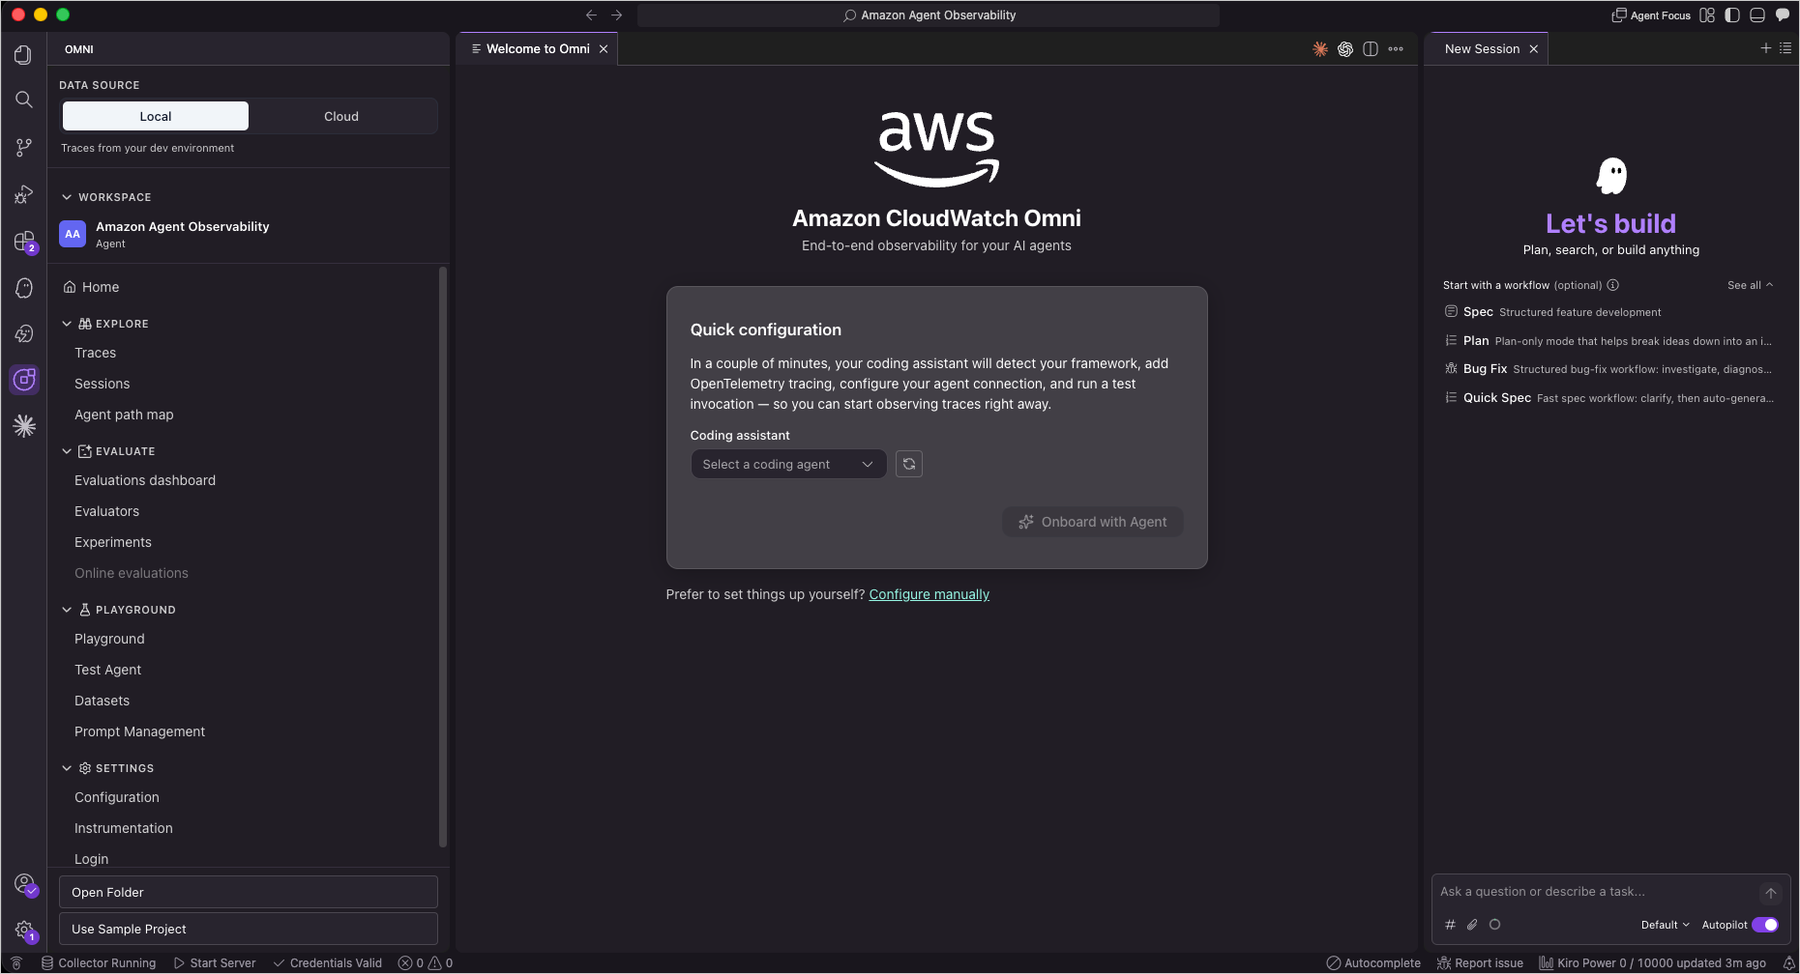
The entire investigation history is captured automatically. No separate incident report needed. Walkthrough: setting up your first Space To set up CloudWatch Omni for your team, open the CloudWatch console and click “Try CloudWatch Omni.”
Figure 1. CloudWatch console — Omni setup page Next, connect your identity provider through IAM Identity Center (supporting Okta, Azure AD, and other SAML 2. 0 providers).
Once connected, your team members access Omni directly at your dedicated URL without needing AWS Console credentials. Create a Space for your team. A Space groups the applications your team owns and the telemetry associated with them.
Figure 2. CloudWatch Omni Home — your team’s workspace with application monitoring, analytics, and agent observability Once created, Omni discovers your services automatically and maps the dependencies between them. You see your application topology immediately.
Figure 3. Application topology — services and dependencies mapped automatically You can ask CloudWatch Omni any question about your applications in plain English, and Omni will analyze your telemetry data and surface insights. Figure 4.
Interact with your telemetry in natural language You can also set up service health alerts, configure what matters to your team, and trigger an AWS DevOps agent investigation to identify the root cause and develop a mitigation plan. Figure 5. Investigation session — DevOps Agent identifies root causes and suggests next steps Application-centric organization CloudWatch Omni organizes telemetry by application rather than by infrastructure component.
The system automatically discovers services from the telemetry data and AWS Config resource discovery, maps dependencies, and lets you see your application as a connected system rather than a collection of isolated resources. Each team gets a Space that contains the applications they own. A Space points at existing CloudWatch data (logs, metrics, traces, and alarms) with no additional data movement required.
Dynamic views replace the maintenance burden of static dashboards, providing ongoing visibility into SLOs and application health. Getting started Getting started takes minutes and doesn’t require reconfiguration of your existing CloudWatch setup.
Originally published at aws.amazon.com